
Can traditional IT cut the cost of cybersecurity solutions?
Where is the line between traditional IT administration and cyber security operations?
Or is there a line at all?


 Key takeawaysKey takeaways are generated with AI assistance. Because automated summaries can occasionally contain errors or miss important context, always refer to the full blog post for complete information.
The article discusses the disconnect between DNS/IT administration and cybersecurity, highlighting how administrative DNS data is often overlooked for security uses. It describes real-world operational challenges where organizations treat DNS as a cost center and cyber security as an extension of IT, citing General Darren McDew’s remarks about reconciling IT administration with cyber priorities. The key outcome recommended is reframing routine DNS administration as a security capability to enable anomaly detection, patient zero identification, and protection of internal network traffic by breaking down organizational silos.
Why do DNS administrators and cybersecurity professionals struggle to collaborate according to the article?
The article explains that DNS administrators prioritize maintaining the pace of operational workflows and view security as secondary, while cybersecurity professionals often see DNS data as purely administrative and not relevant to threat detection. This mutual perception creates a boundary where DNS is treated as a cost-center infrastructure task, and cyber is treated as an added expense or separate function. The result is organizational silos and competition for scarce resources, which inhibits collaboration and prevents full recognition of DNS data’s security value.
What security benefits can come from using administrative DNS data as described in the article?
According to the article, leveraging administrative DNS data within a cybersecurity context enables anomaly detection, helps identify “patient zero” events, and supports protection of internal network traffic. By analyzing DNS logs and administrative records, teams can detect unusual query patterns or resolution behavior that indicate compromise or data exfiltration. Integrating these DNS-centric tasks into security workflows transforms routine administration into proactive threat detection and network protection capabilities.
What organizational change does the article suggest to better leverage DNS for security?
The article recommends reframing day-to-day DNS network administration as a component of cybersecurity rather than treating it solely as IT infrastructure overhead. It advocates breaking down silos between IT administration and security teams so routine DNS tasks are executed in the context of threat detection and mitigation. This vision requires cultural change and leadership recognition—echoed by General McDew’s experience—that true transformation comes from valuing DNS as a core security capability and aligning resources and processes accordingly.
Or is there a line at all?
Those who use administrative DNS data to analyze and mitigate anomalies are relevant to both IT management and IT security.
But straddling that boundary isn’t always easy. More often than not, DNS administrators are focused on maintaining the pace of their workflow and view security as a secondary priority.
It cuts the other way, too. IT security professionals tend to overlook DNS data as a purely administrative function with little relevance to countering threats.
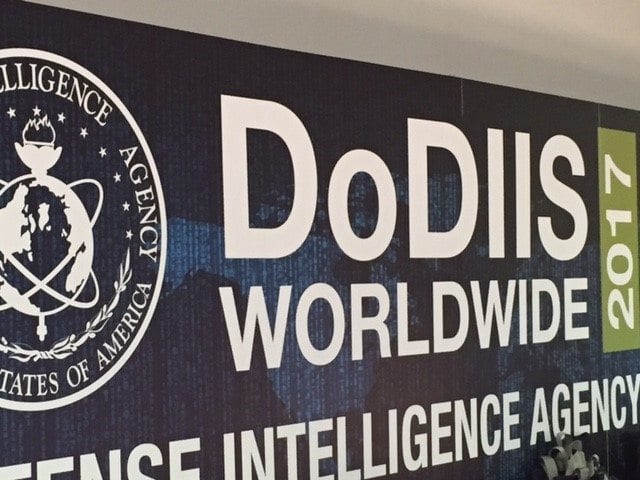
Here at the DODIIS 2017 conference, we heard from General Darren McDew, Commander of US Transportation Command, who eloquently summarized his own struggles to reconcile day-to-day IT administration with cyber security.
“I viewed cyber through the lens of IT,” he said, shaking his head. In a competition for scarce resources, Transportation Command treated cyber security as an extension of IT administration costs rather than recognizing it as a core capability.
The same thing can be said about DNS at the enterprise level. So many large organizations view DNS as a cost center – part of the core infrastructure which keeps networks up and running. Nothing more.
This is cyber security through the lens of IT.
DNS and CyberSecurity
There is a better approach: move day-to-day DNS network administration tasks into the context of cyber security.
By realizing and leveraging the value of DNS data for anomaly detection, “patient zero” identification, and protection of internal network traffic, traditional barriers between traditional IT administrators and their cyber security colleagues can be broken down.
It’s a question of vision. General McDew recognized that cyber security viewed through the lens of IT undervalued the entire network enterprise. True transformation requires IT professionals to break through organizational silos to realize the security value of the tasks they perform every day.
We know this isn’t always a comfortable or easy process; but we agree the journey is worthwhile.
Published in:

BlueCat provides core services and solutions that help our customers and their teams deliver change-ready networks. With BlueCat, organizations can build reliable, secure, and agile mission-critical networks that can support transformation initiatives such as cloud adoption and automation. BlueCat’s growing portfolio includes services and solutions for automated and unified DDI management, network security, multicloud management, and network observability and health.
Related content
Get answers from the LiveNX data you already have with LiveAssist
Learn how LiveAssist, the AI-powered add-on for LiveNX, turns your network data into fast, guided answers, with value you can see in days.
LiveWire GEN3 device offerings
BlueCat LiveWire is a packet capture and network forensics platform that provides deep packet-level visibility across hybrid enterprise environments to help…
Get total control of your DDI infrastructure with Micetro’s unified API
Stop juggling between network tools and use Micetro’s RESTful API for complete control over your DDI infrastructure and cloud environment.
BlueCat MCP servers bring network intelligence to your AI assistant
Our MCP servers provide a standard integration layer that makes it easy to connect the AI tools you already use to BlueCat products.