
Blog
DNS glossary

 Key takeawaysKey takeaways are generated with AI assistance. Because automated summaries can occasionally contain errors or miss important context, always refer to the full blog post for complete information.
NSD (name server daemon) is an open-source authoritative-only DNS server developed by NLnet Labs that answers queries for configured zones without performing recursion or caching, making it lightweight and secure for organizations that pair it with a separate recursive resolver. By design, NSD eliminates the open recursion vulnerability common in combined authoritative-recursive servers, and its narrow focus simplifies code maintenance, capacity planning, and attack surface. Organizations must manage zone consistency through proper DNS NOTIFY and zone transfer configuration, monitor for stale secondaries and transfer failures, and ensure firewall rules permit both UDP and TCP on port 53 to support full DNSSEC validation and large responses.
NSD loads zone data it is configured to serve and answers queries for those zones. It does not resolve names on behalf of clients, so it never queries other servers to find answers for zones it does not hold.
NSD can serve DNSSEC-signed zones, but zone signing is handled by separate tooling. Because it is authoritative only, organizations pair it with a separate recursive resolver for client lookups.
A secondary NSD instance keeps serving an old zone version when NOTIFY messages are blocked or the primary's serial was not incremented. Symptoms are different answers from different name servers for the same name.
Zone transfers fail when the primary's allow-transfer settings, firewall rules or TSIG key and algorithm do not match the secondary's configuration. Logs on the secondary show repeated transfer failures and the zone never loads.
A typo in a zone file can leave a zone unloaded or keep the previous version in service after a reload. Running the bundled zone and configuration checking tools before reloading catches most of these.
Firewalls that permit only UDP on port 53 break zone transfers and large or truncated responses, including many DNSSEC answers. Clients then see intermittent failures only for big responses.
Clients pointed at an NSD host as their resolver get refused or empty answers for names outside its zones. NSD does not recurse, so a separate resolver must serve client lookups.

 Article
An authoritative DNS server provides original and definitive answers to DNS queries.
Article BIND is widely-used software that publishes DNS information on the internet and resolves DNS queries for users.
Article A recursive DNS server is the first server contacted by a requesting host; it retrieves the proper IP address of the intended domain name and returns it to the requester.
Article A DNS zone is a contiguous portion of the domain name space for which administrative responsibility and authority have been delegated to a single manager.
Article TSIG (transaction signature) is a protocol that enables DNS to authenticate updates to a DNS database, most commonly for dynamic DNS or secondary DNS servers.
Article DNSSEC (Domain Name Service Security Extension) is a mechanism that uses cryptography to authenticate DNS data and verify the integrity of DNS queries and responses.
Article An NS record is a DNS record that provides a list of the authoritative name servers responsible for a domain.
Article An SOA record is a DNS record type that provides important details about a DNS zone and is required for every DNS zone.
DNSSEC authenticates DNS queries and responses by using cryptographic digital signatures. Learn more and how BlueCat can help to make implementation easier.
Read more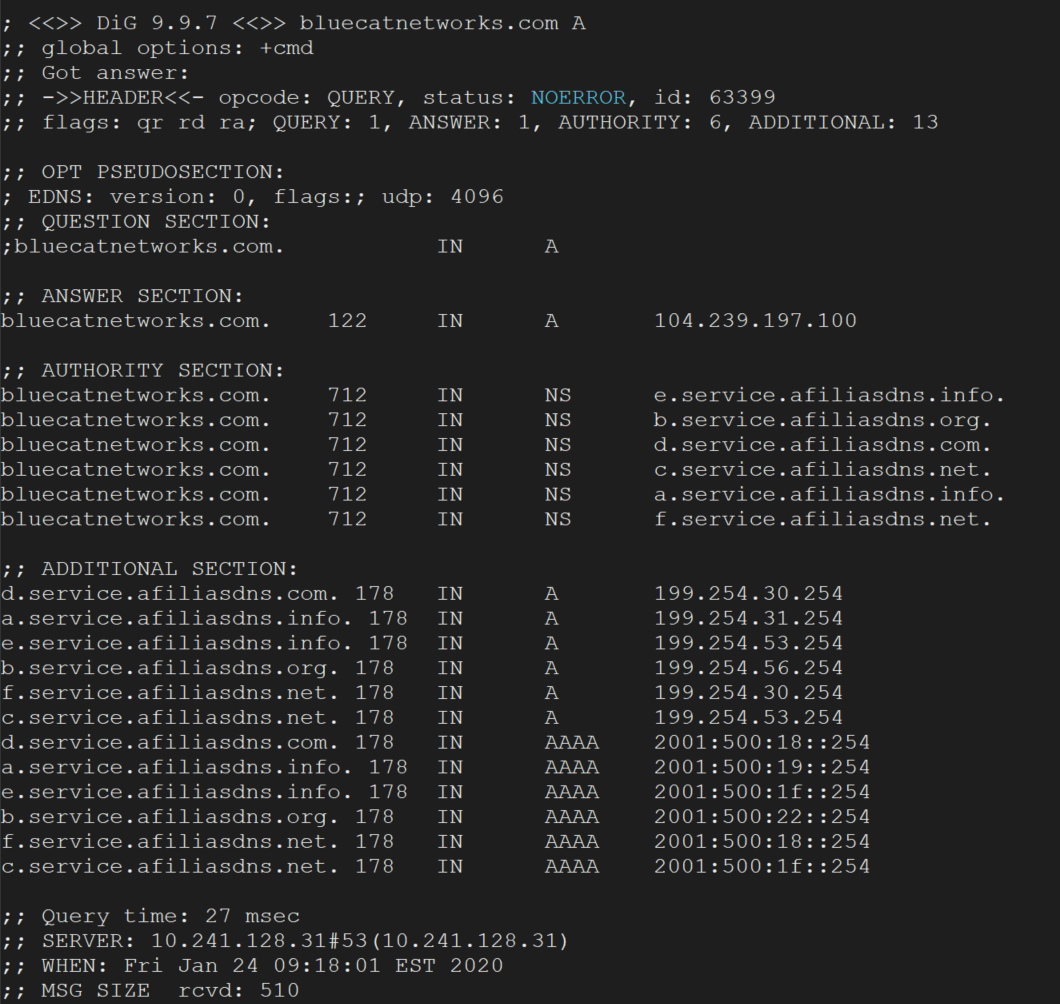
There are dozens of DNS record types. Understanding the most common ones can help you detect threats and keep on top of what's happening…
Read more
This eBook outlines the journey from the functional to the inevitable, when you realize your “free” Microsoft DNS is anything but.
Read more
Global Server Selector provides easy configuration and automatically updates DNS for highly available access to distributed applications and services.
Read more
At a basic level, an NXDOMAIN response means “that site does not exist.” But it can also provide critical clues about your network’s security.
Read more