Security glossary

What is RADIUS (Remote Authentication Dial-In User Service)?

Abstract isometric UI showing network ranges, usage bars, region names (EMEA/APAC), and a purple "Deploy" button
Key takeawaysKey takeaways are generated with AI assistance. Because automated summaries can occasionally contain errors or miss important context, always refer to the full blog post for complete information.

RADIUS (Remote Authentication Dial-In User Service) is a network protocol that centralizes authentication, authorization, and accounting for users and devices accessing enterprise networks through Wi-Fi, wired 802.1X, and VPN gateways. A network access server acts as the RADIUS client, forwarding user credentials to a central RADIUS server, which returns an access decision and authorization attributes such as VLAN assignments or session timeouts. Organizations depend on RADIUS to enforce consistent access policies across multiple network devices from different vendors, but must manage server redundancy, shared secret security, and potential configuration issues like certificate failures or port mismatches to ensure reliable authentication and prevent login failures or data exposure.

  • RADIUS operates over UDP on ports 1812 (authentication) and 1813 (accounting), with the shared secret protecting only the password attribute while other message attributes remain unencrypted unless additional protection via EAP, IPsec, or TLS is implemented.
  • Common deployment failures stem from mismatched shared secrets between client and server, server unreachability due to firewall or routing issues, missing or incorrect authorization attributes, and EAP certificate expiration that blocks authentication for many devices simultaneously.
  • Organizations must configure redundant RADIUS servers on each network device and establish failover testing procedures before outages occur, since a single-server dependency can block all new logins and reauthentication when the server becomes unavailable or enters maintenance.

RADIUS at a glance

AttributeValue
Full nameRemote Authentication Dial-In User Service
CategoryNetwork protocol
Defined inRFC 2865 (authentication and authorization) and RFC 2866 (accounting)
Protocol and portUDP ports 1812 for authentication and 1813 for accounting; older deployments used ports 1645 and 1646
OSI layerApplication layer (layer 7)
Primary useCentralized authentication, authorization, and accounting for network access such as Wi-Fi, VPN, and wired 802.1X
Related termsAAA, 802.1X, EAP, TACACS+, Network access control

How RADIUS works

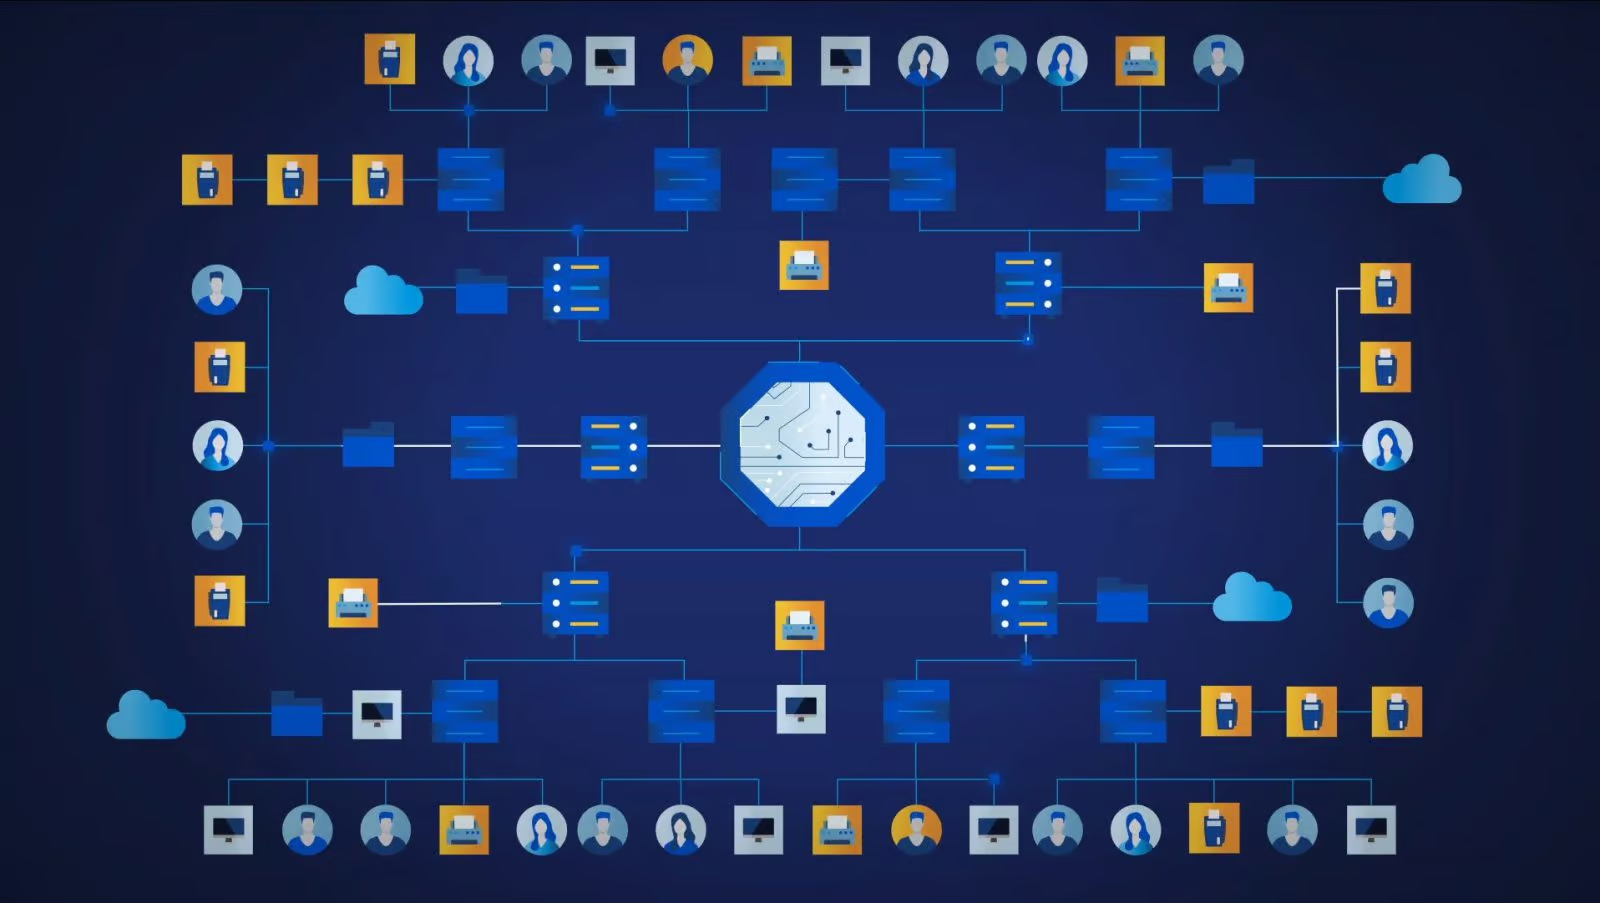
RADIUS works between a network access server, which acts as the RADIUS client, and a central RADIUS server. The client never checks credentials itself; it forwards them and enforces the answer.

  1. Access request: A user or device connects to a switch, wireless controller, or VPN gateway. That device, acting as the RADIUS client, sends an Access-Request containing the credentials or EAP data plus attributes such as the client identifier.
  2. Server evaluation: The RADIUS server checks the request against its user store, such as a directory or database, and applies its policies. Requests are authenticated between client and server using a shared secret.
  3. Server response: The server replies with Access-Accept, Access-Reject, or Access-Challenge. A challenge asks for more information, such as a second factor or the next step in an EAP exchange.
  4. Authorization attributes: An Access-Accept can carry attributes that tell the client what to grant, such as a VLAN assignment, session timeout, or filter rule.
  5. Accounting: The client sends Accounting-Request messages when a session starts, updates, and stops. The server records usage data for auditing and billing.

RADIUS runs over UDP, so deployments usually configure timeouts, retries, and backup servers. Only the password attribute is obscured with the shared secret, so RADIUS traffic should be carried over protected links, or over TLS where supported.

Why RADIUS matters in enterprise networks

RADIUS is the common mechanism behind enterprise Wi-Fi login, wired 802.1X port security, and remote access VPN. Because it is standardized in RFC 2865 and RFC 2866, switches, controllers, and gateways from many makers can all point at one policy server. That removes per-device local accounts and lets an organization change who has access, and under what conditions, in one place.

The central server becomes a dependency for every login. If it is unreachable, new users and devices cannot join the network, and reauthentication can drop existing sessions. Teams typically run redundant servers, tune timeouts, and monitor response times. Mismatched shared secrets, clock or certificate problems in EAP deployments, and wrong client address entries are common causes of failed authentication.

Security depends on configuration. The shared secret protects message integrity between client and server, so weak or reused secrets across many devices weaken that protection. Because the protocol obscures only the password attribute, an exposed path can leak other user data. Strong EAP methods, protected transport, and logged accounting records limit these risks and support incident investigation.

RADIUS vs AAA (Authentication, Authorization and Accounting)

AAA is the general framework of authenticating, authorizing, and accounting for access, while RADIUS is one specific protocol that implements that framework. What is AAA?

AttributeRADIUSAAA (Authentication, Authorization and Accounting)
TypeNetwork protocolConceptual framework
Defined inRFC 2865 and RFC 2866Not a single specification; implemented by several protocols
ScopeCarries requests, decisions, and accounting records between client and serverDescribes the three functions any access control system performs
ExamplesRADIUSRADIUS, TACACS+, and Diameter

RADIUS vs Lightweight Directory Access Protocol (LDAP)

RADIUS decides whether a device or user may access the network, while LDAP is a protocol for reading and querying a directory that often holds the identities RADIUS checks. What is LDAP?

AttributeRADIUSLightweight Directory Access Protocol (LDAP)
Primary roleNetwork access authentication, authorization, and accountingDirectory lookup and update
Typical clientSwitch, wireless controller, or VPN gatewayApplications and servers
RelationshipOften queries a directory for credentials and group membershipOften serves as the user store behind a RADIUS server
AccountingSupported through accounting messagesNot part of the protocol

Common RADIUS issues

If the secret on the network device differs from the one configured for that client on the server, requests fail or are dropped. Server logs often show packets with an invalid authenticator, and users see repeated login failures even though their credentials are correct.

A firewall rule, routing change, or wrong source address can stop requests from reaching the server. Switches and controllers then time out and may fall back to a guest VLAN, local account, or no access, depending on configuration.

Users authenticate successfully but land in the wrong VLAN or role because the server returns an attribute the device does not honor, or none at all. Vendor-specific attribute names and values often differ between device makers.

With only one RADIUS server configured, a failure or maintenance window blocks new logins and reauthentication. Configure at least two servers on each client and test failover behavior before an outage does it for you.

In 802.1X deployments using certificate-based EAP methods, an expired server certificate or a client that does not trust its issuer causes authentication to fail for many devices at once. The cause is usually the certificate, not the user accounts.

See how unified DDI simplifies network operations

Manage DNS, DHCP and IP addresses from one platform with automation, visibility and control built in.

RADIUS FAQ

Related terms

Article

AAA (Authentication, Authorization and Accounting)

Refers to a family of protocols that mediate network access.

Learn more
Article

Lightweight Directory Access Protocol (LDAP)

An open, vendor-neutral, industry standard application protocol for accessing and maintaining distributed directory information services over an IP network.

Learn more
Article

Active Directory

A Microsoft directory service for Windows domain networks that is included in most Windows Server operating systems as a set of processes and services.

Learn more
Article

User Datagram Protocol (UDP)

An alternative protocol to TCP used primarily for establishing low-latency and loss-tolerating connections between applications on the internet.

Learn more
Article

Transport layer security (TLS)

A cryptographic protocol to provide communications security over a computer network.

Learn more
Article

ACL (Access Control List)

Limits which entities are allowed to perform certain functions against a DNS server, such as sending queries or performing dynamic updates.

Learn more
Article

DMZ (Demilitarized zone)

A subnetwork that contains and exposes an organization’s external-facing services to an untrusted, usually larger, network such as the internet.

Learn more
Article

High Availability (HA)

It aims to ensure a certain level of operational performance or uptime for a system.

Learn more