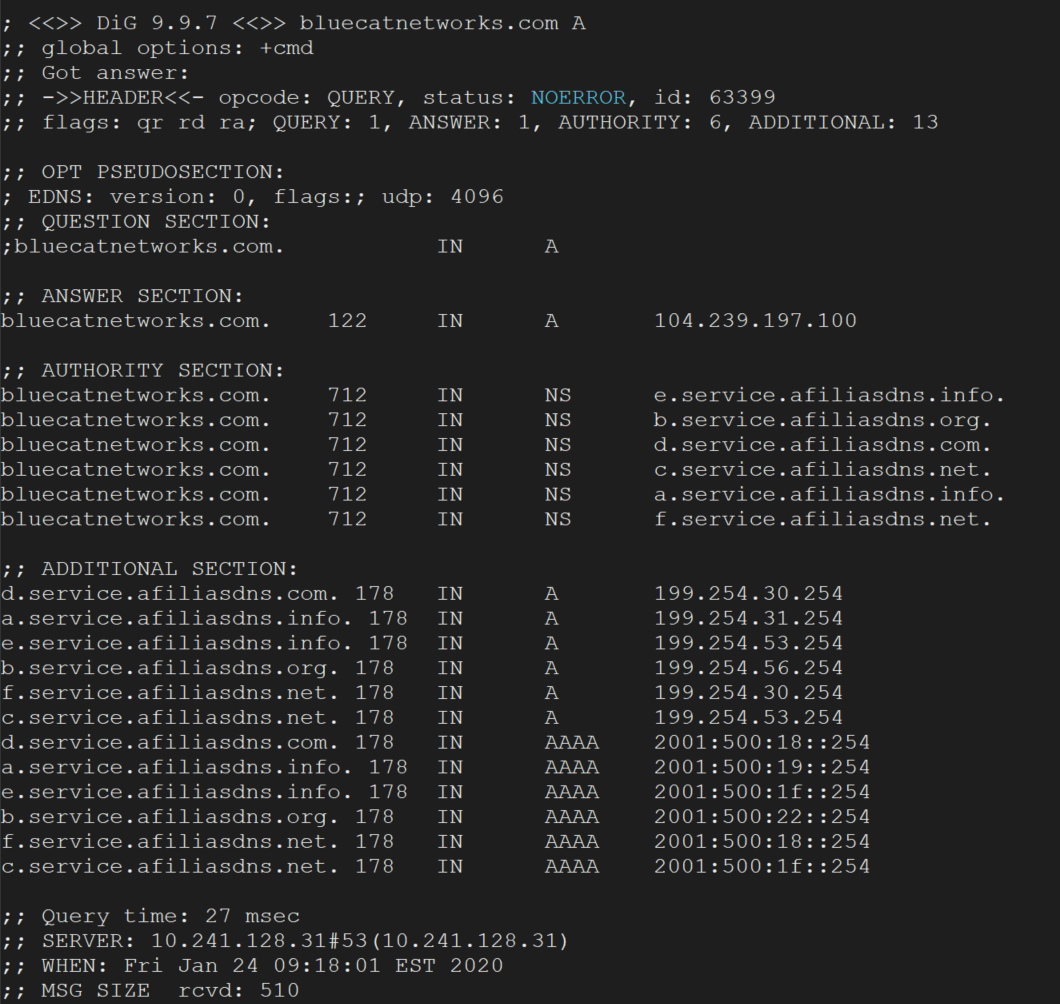
Know the eight most common DNS record types
There are dozens of DNS record types. Understanding the most common ones can help you detect threats and keep on top of what's happening…
Read moreRFC 1918 networks define three reserved IPv4 address ranges (10.0.0.0/8, 172.16.0.0/12, and 192.168.0.0/16) that organizations can use internally without public registration, conserving scarce global address space for enterprises, campuses, and cloud networks. These private addresses are not routed on the public internet and require network address translation or a proxy to reach external hosts, but create operational risks when multiple networks merge or connect via VPN because the same ranges can be reused by many organizations, leading to overlapping subnets. Careful IP address management and central planning in IPAM systems are essential to prevent conflicts, duplicate assignments, and the slow, error-prone process of renumbering or adding translation to resolve address space collisions.
RFC 1918 reserves three IPv4 blocks for private use. Hosts in these blocks communicate freely inside a network, and internet access depends on how the network is connected to the outside.
The three reserved blocks are 10.0.0.0 to 10.255.255.255 (10.0.0.0/8), 172.16.0.0 to 172.31.255.255 (172.16.0.0/12), and 192.168.0.0 to 192.168.255.255 (192.168.0.0/16). Any organization can use them without asking a registry, and routers on the public internet are expected not to forward traffic to or from them. Because many networks use the same ranges, addresses are only unique within one network. To reach public destinations, a host usually goes through a gateway that performs network address translation or a proxy, which presents a public address on its behalf. When two private networks are joined, by a VPN or a merger, overlapping ranges must be resolved by renumbering or translation.
Two organizations that both use 10.0.0.0/8 or 192.168.0.0/16 often find the same subnet on both sides when they connect. Symptoms include traffic that stays local instead of crossing the link, and the fix is renumbering or translating one side.
A remote user's home network commonly uses 192.168.0.0/24 or 192.168.1.0/24, which can collide with the same corporate subnet. Routes to the office then fail or point to the local network. Multi-cloud peering fails for the same reason when virtual networks share a range.
Misconfigured filters or DNS records can expose RFC 1918 addresses to outside parties. Outsiders then see unreachable answers, or traffic sourced from private addresses appears at the edge and is dropped.
Teams that assign small or arbitrary subnets from the 10.0.0.0/8 block without a plan run out of contiguous space and cannot summarize routes. Tracking allocations in IPAM prevents this and shows conflicts before deployment.
Queries for private addresses that escape the internal network reach public resolvers, which cannot answer them usefully. This produces slow lookups and noisy logs, and internal resolvers should be authoritative for these reverse zones.