The OSI model splits networking into seven layers, and core network functions operate at different layers, with DNS at Layer 7, IP addressing at Layer 3 and MAC addressing at Layer 2. BlueCat Integrity links MAC and IP records in one source of truth.
· 01 — What the OSI model is and how its seven layers divide the work
What is the OSI model?
The OSI model is a conceptual framework, created by the International Organization for Standardization, that divides network communication into seven stacked layers.
Each layer performs a distinct function and communicates with the layers directly above and below it.
From the top, the layers are application (Layer 7), presentation (6), session (5), transport (4), network (3), data link (2) and physical (1). The model is independent of specific protocols, unlike the four-layer TCP/IP model built around internet protocols, and it gives engineers a common language for troubleshooting.
DNS is an application layer protocol at Layer 7. It travels over UDP, and sometimes TCP, at Layer 4 and over IP at Layer 3. This can cause confusion, but using those layers does not make DNS a Layer 4 or Layer 3 protocol.
7abstract layers
7 abstract layers
The model stacks seven layers, from the electrical, radio or optical signals of Layer 1 up to the application protocols of Layer 7.
The OSI model is a conceptual model that provides a universal standard for how computing devices communicate across networks, with seven abstract layers.
1 min·Page
Read more →
· 02 — Why the OSI model is a reference and not a network
What do people get wrong about the OSI model?
The most common mistake is treating the OSI model as a network that something can connect to.
It is a seven-layer model for networking, and the data link layer is its second layer, not something a network connects to.
Confusion about layers also leads people to conflate protocols that do very different jobs. ARP is a data link layer protocol that resolves an IP address to a MAC address, while DNS is a hierarchical naming system that translates domain names into IP addresses. The two are separate, though IP networks need working ARP for DNS to work.
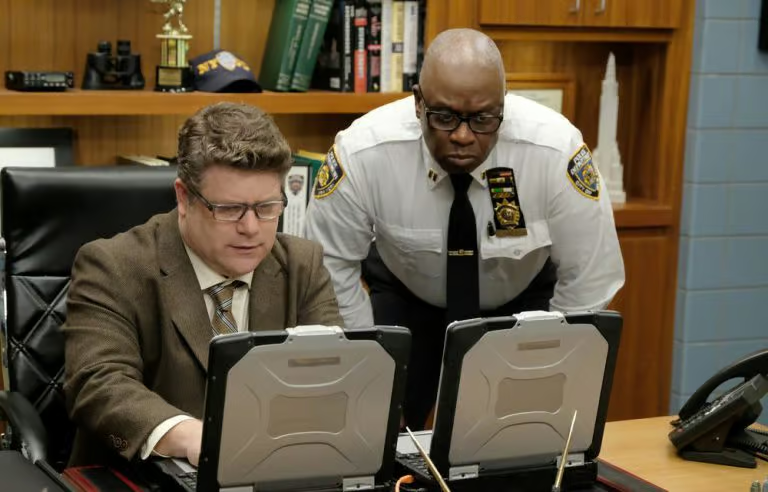
One episode (S6E14) of Brooklyn Nine-Nine, a TV crime comedy, combined these terms nonsensically and earned a line-by-line fact-check, including the reminder that OSI isn’t a network. The episode’s broader lesson concerned social engineering, with an attacker who nearly succeeded because the team lacked the technical knowledge to question him.
Brooklyn Nine-Nine's writers have a great cybersecurity vocabulary, but not a great understanding of how cybersecurity works. BlueCat breaks it down.
8 min·Blog
Read more →
· 03 — What encrypting DNS changes for the teams that watch it
What happens to DNS visibility when queries are encrypted over HTTPS?
Enterprise visibility into DNS drops to zero.
DNS over HTTPS carries ordinary DNS queries and responses inside HTTPS encryption, so anyone watching along the path, including enterprise security tools, can no longer tell which names are being resolved.
In normal resolution, a device asks a recursive resolver for an address, and the resolver may query a chain of nameservers until one answers. Network teams read those queries to monitor network health and optimize resolution paths, and many organizations inspect them as part of a DNS security strategy.
Encrypting that traffic protects users from eavesdropping along the network path, but on enterprise networks it can prevent cybersecurity solutions from inspecting DNS queries and make routing by query content far harder. It also concentrates resolution on a few public resolvers, so a single outage could affect far more people.
Encrypting DNS queries and responses over HTTPS has long sparked robust debate, with interest from numerous stakeholders. Learn more with BlueCat.
8 min·Blog
Read more →
· 04 — How attackers turn open DNS into a denial-of-service amplifier
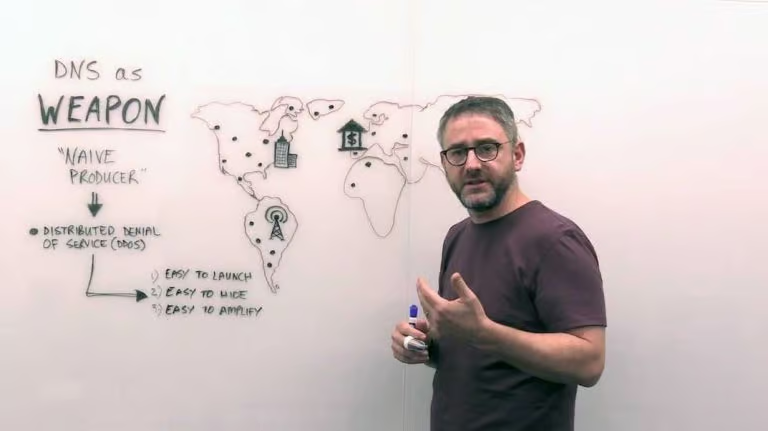
How do DDoS attacks use DNS as a weapon?
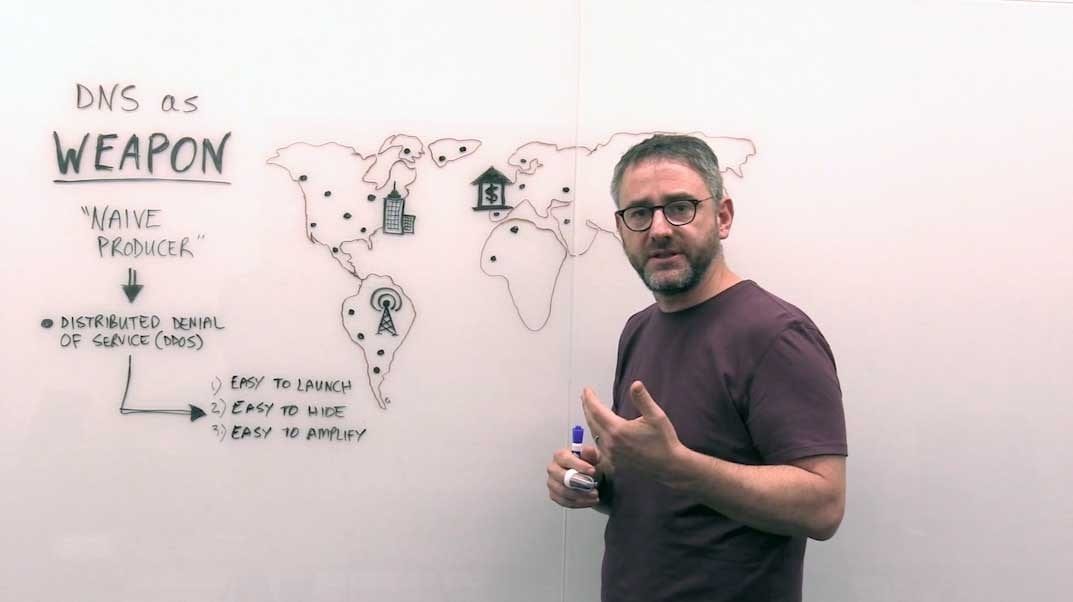
Attackers use DNS because it is open by design, and its queries are inexpensive to generate and easy to spoof.
Spoofed queries sent through open resolvers turn DNS servers into amplifiers that flood a victim with far larger responses than the requests that triggered them.
DDoS attacks take three forms: protocol attacks that exhaust servers, firewalls or load balancers, application layer attacks that send legitimate-looking requests to crash web servers, and floods of spoofed packets. Botnets of compromised computers and IoT devices supply the volume, sometimes hundreds of thousands of hosts or more.
DNS is an attractive target for attackers because it has to stay open, and resolvers must process every request to do their job. Most security teams also take the protocol for granted and leave it unmonitored, which is exactly the gap attackers count on.
70:1amplification ratio
70:1 amplification ratio
For roughly every 80 bytes an attacker sends, DNS can generate about 5.6 kilobytes of attack traffic.
Bad actors know that DoS and DDoS attacks can use DNS as a weapon to cause spectacular web crashes that bring critical business services to their knees.
7 min·Blog
Read more →
We work with enterprise teams consolidating DNS, DHCP, and IPAM onto BlueCat Integrity. A 30-minute call can help you assess your network’s needs.
· 05 — What a platform needs to make DNS visible across the enterprise
What should teams look for in a platform for DNS visibility and troubleshooting?
The core requirement is DNS data from every server in one searchable place, with the ability to trace a query along its path between clients, networks and servers.
Without both, the patterns that reveal infections and misconfigurations stay buried in individual logs.
Persistent NXDOMAIN answers from one endpoint can point to malware beaconing or to reconnaissance and lateral movement, while zones that fall out of sync return NXDOMAIN to some users and correct answers to others. With the right logs, those failed responses become a valuable source of information.
Zones that fall out of sync are hard to troubleshoot without visibility into east-west traffic.
At a basic level, an NXDOMAIN response means “that site does not exist.” But it can also provide critical clues about your network’s security.
5 min·Blog
Read more →
· 06 — How one record links Layer 2 hardware to Layer 3 addresses
How do enterprise teams trace a device across Layer 2 and Layer 3 without spreadsheets?
They keep MAC and IP addresses in one system of record instead of a spreadsheet.
A MAC address identifies hardware at Layer 2 and an IP address identifies a network connection at Layer 3, so linking the two lets teams troubleshoot at the device level.
On a LAN, ARP bridges the two layers by mapping IPv4 addresses to MAC addresses, and IPv6 uses Neighbor Discovery for the same job. Large enterprises can manage millions of MAC and IP addresses, yet some still track IP addresses in spreadsheets and overlook MAC addresses, creating significant operational risk.
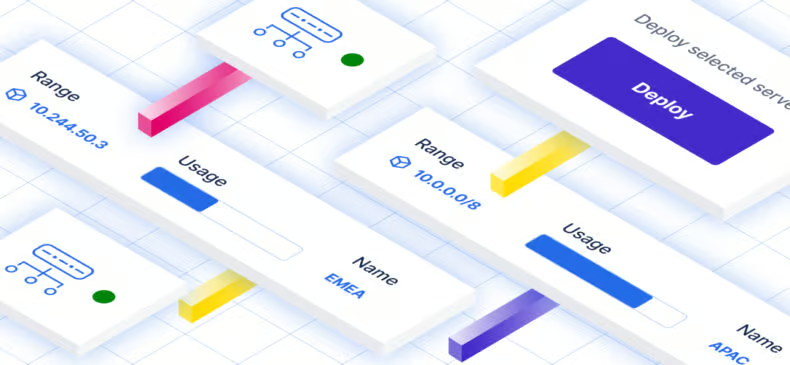
BlueCat Integrity unifies DNS, DHCP and IPAM to provide one source of truth for relationships between devices, users and IP addresses. Its Address Manager lets admins record MAC addresses, group them into MAC pools and link each to IP addresses across networks, so troubleshooting can start at the device.
Tame network complexity with Integrity's full-stack DDI management platform and get visibility and control over your DNS, DHCP, and IPAM.
9 min·Page
View Integrity →
· 07 — Paths forward
Which path is right for making core network services easier to troubleshoot layer by layer?
The right starting point depends on the problems your team faces today, including confusion about which layer a problem occurs at, limited visibility into DNS traffic, or addresses tracked by hand. Each path below addresses one of those gaps.
PATH 01
Teams describe the same outage in different terms
Agree on the layers before the incident
Use the seven layers as the shared language for triage, so a fault is identified by the layer where it occurs. Keep ARP and DNS separate in runbooks and remember that DNS stops working whenever ARP does.
Users or browsers may already be resolving names over HTTPS
Decide how encrypted DNS is handled
Treat encrypted DNS as a policy choice rather than a default discovered later. Where visibility matters more, block known DNS over HTTPS resolvers with a response policy zone so queries stay on resolvers teams can monitor.
Monitor DNS logs so the network is not used to attack others, control which requests are allowed to resolve, and centralize the data so NXDOMAIN patterns can be analyzed in context. Infrastructure that can add bandwidth or divert malicious queries limits the damage when an attack occurs.
IP addresses live in spreadsheets and MAC addresses are not tracked
Link every address to its hardware
Move both into one system of record so each MAC address is linked to its associated IP addresses across networks. Troubleshooting can then start at the device rather than at the symptom.
Short answers to the questions engineers most often ask about the OSI model and the services that run across it.
The seven layers, from top to bottom, are application (Layer 7), presentation (6), session (5), transport (4), network (3), data link (2) and physical (1). A common mnemonic is All People Seem To Need Data Processing. Not every exchange uses all seven, and only Layers 1, 2 and 3 are mandatory.
DNS is an application layer protocol at Layer 7. It travels over UDP, and sometimes TCP, at Layer 4 and over IP at Layer 3, usually on port 53. Using those layers does not make DNS a Layer 4 or Layer 3 protocol.
The OSI model has seven layers and is independent of any specific protocol, so it can describe any form of network communication. The TCP/IP model, created by the US Department of Defense, collapses several OSI layers into four and is specific to internet protocols.
MAC addresses are implemented in the MAC sublayer of the data link layer, Layer 2, and IP addresses operate at the network layer, Layer 3. On IPv4 networks, ARP maps one to the other, and IPv6 uses Neighbor Discovery instead. BlueCat Integrity keeps the two linked in one record, with its Address Manager tying each MAC address to the IP addresses it uses across networks.
NXDOMAIN means the domain name in a DNS query does not exist, and only an authoritative nameserver can return it. For one user it usually means a typo, but persistent NXDOMAIN patterns can point to malware beaconing, reconnaissance or DNS zones that have fallen out of sync.
Yes. DNS over HTTPS encrypts queries and responses inside HTTPS, so enterprise security and network tools lose sight of which names are being resolved. The resolver handling the encrypted traffic still sees them, and other signals such as IP addresses remain exposed. Teams that want that visibility back can block known DoH resolvers in BlueCat Integrity, using a response policy zone with BlueCat’s DoH threat feed.
We’re using cookies on this website to improve your experience. Cookies help us learn how you interact with our website and remember you when you come back so we can tailor it to your interests.
To learn more about cookies and how we use them, read our cookie notice.
Some cookies are essential, while others help us to improve your experience by giving us insight into how you are using our website. You may adjust your preferences for non-essential cookies below.
To learn more about cookies and how we use them, read our cookie notice. You can also review our privacy policy for more details on the personal data we collect, use, hold, and disclose when you visit our website or use our products and services.
Functional cookies
Functional cookies are essential cookies that allow us to remember choices or changes you have made (such as to language settings or your choices regarding the use of cookies). These cookies cannot be turned off since they are essential for the operation of our Websites.
Analytics cookies
Analytics cookies are non-essential cookies that collect information on how visitors use our Websites. We use this information with your consent to measure the number of visitors to our Websites, determine whether specific content or communication has been viewed, and to help us improve our Websites and communication. These cookies can be turned off.
Personalisation Storage
Personalisation cookies are non-essential cookies that collect information when you fill out a form on this website. We only use this information with your consent to pre-fill other forms on the site. These cookies can be turned off.
Marketing cookies
Marketing cookies are cookies that are placed by third parties to collect information about your visits and actions on our Websites so that they or we can deliver ads to you later, such as when you are on certain third-party sites or platforms. These cookies may be used by those third parties to build a profile of your interests and show you relevant ads on other websites. These cookies also enable visitors to our Websites to share content on social networks and to enable and evaluate interactions with our communication and social media tools. These cookies can be turned off.