
Dispatch from DoDIIS 2017: The Incredible Shrinking Decision Space
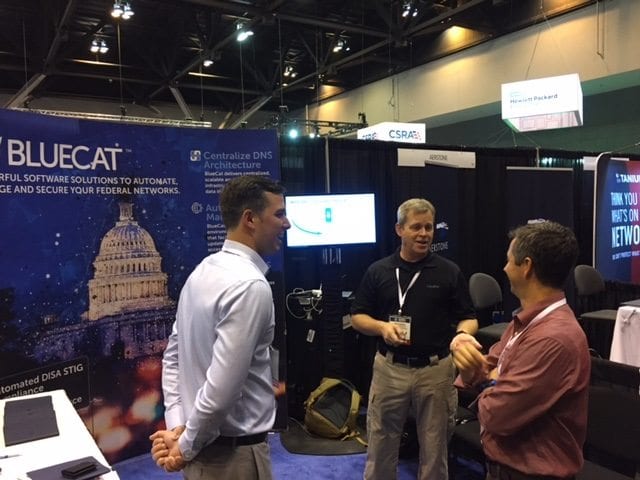
Here at the DoDIIS 2017 conference, we’re hearing a lot about the role of cybersecurity in so-called “fifth generation warfare” – a concept with direct relevance to the power of DNS for network security.


 Key takeawaysKey takeaways are generated with AI assistance. Because automated summaries can occasionally contain errors or miss important context, always refer to the full blog post for complete information.
At DoDIIS 2017, speakers examined how fifth generation warfare — where digital and physical battlefields blur and cyber and kinetic attacks are coordinated — threatens military decision space by constraining network availability. The article explains that enterprise DNS, when centrally monitored and managed, is a critical tool for detecting subtle indicators of compromise (beaconing, unusual data transfers, and suspicious queries) and for maintaining network resilience during attacks. By leveraging active DNS-based security, DOD and intelligence IT teams can expand leaders' decision space with a resilient and maneuverable network architecture centered on DNS.
What is fifth generation warfare and how does it relate to DNS-based cybersecurity?
Fifth generation warfare blurs the lines between digital and physical battlefields, combining cyberattacks with kinetic operations to constrain an opponent’s ability to respond. In this environment attackers may infiltrate networks over time and activate capabilities to limit network availability at decisive moments. Centrally monitored and managed DNS is relevant because it sits at the core of network architecture and can surface subtle indicators of compromise—such as beaconing to external IPs, unusual data transfers, and queries for sensitive resources—helping detect and mitigate cyber operations that are part of fifth generation warfare.
How can enterprise DNS help detect an ongoing network breach?
Enterprise DNS can reveal early and subtle signs of a breach by logging and correlating name resolution activity across the network. Indicators include persistent beaconing patterns to external addresses, anomalous or large-scale zone transfers, and queries targeting sensitive segments or services. When DNS is centrally monitored and managed, these patterns become visible to IT security personnel, enabling earlier detection of infiltration that might otherwise ‘simmer in the background’ until called into action, and providing actionable intelligence to contain and investigate malicious activity.
In what ways does DNS contribute to network resilience during coordinated cyber and kinetic attacks?
DNS contributes to resilience by rapidly identifying and isolating the operational impact of cyberattacks from the network core. A resilient DNS architecture allows defenders to annul malicious effects—such as redirecting or blocking harmful name resolutions, preventing exfiltration routes discovered via DNS logs, and restoring critical name services—so that affected systems remain manageable. As Lieutenant General Vincent Stewart described, having a centrally managed, DNS-centered network supports a ‘resilient and maneuverable’ posture that expands the decision space available to military and political leaders during coordinated attacks.
Here at the DoDIIS 2017 conference, we’re hearing a lot about the role of cybersecurity in so-called “fifth generation warfare” – a concept with direct relevance to the power of DNS for network security.
In the fifth generation warfare concept, boundaries between the digital battlefield and the physical battlefield are blurred. Cyberattacks and kinetic attacks happen in tandem, with the goal of taking down critical networks to limit the opposing military’s ability to respond.
Lieutenant General Vincent Stewart, Director of the Defense Intelligence Agency, spoke about how this emerging type of warfare “shrinks the decision space” for any military or political response in the event of an attack.
In the cyber world, this often means constraining the enemy’s network availability when troops on the ground are acting. General Stewart used Russia’s actions in the Crimean peninsula as an example; as the “little green men” came in on the ground, Russia’s cyber warriors were constraining the Ukrainian government’s ability to respond effectively.
This kind of offensive cyber warfare rarely happens all at once. Infiltrating an opponent’s network often takes place over time, simmering in the background until it is called to action (as it was in Ukraine).
In this environment, enterprise level DNS data is a critical tool for both preventing cyberattacks and establishing resilience when attacks hit.
Sitting at the core of the network’s architecture, a centrally monitored and managed Domain Name System can detect the subtle indications of a breach, “beaconing” pings of outside IP addresses, unusual transfers of data, and searches for sensitive areas of the network – signaling malicious activity. DNS also plays a critical role in network resilience, quickly identifying and annulling the impact of a cyberattack from the network’s core infrastructure.
With in active DNS-based security in place, DOD and intelligence IT security personnel can actively expand the decision space of the political leaders they support. General Stewart’s ideal network – “resilient and maneuverable” – has DNS at its core.

BlueCat provides core services and solutions that help our customers and their teams deliver change-ready networks. With BlueCat, organizations can build reliable, secure, and agile mission-critical networks that can support transformation initiatives such as cloud adoption and automation. BlueCat’s growing portfolio includes services and solutions for automated and unified DDI management, network security, multicloud management, and network observability and health.
Related content
Get answers from the LiveNX data you already have with LiveAssist
Learn how LiveAssist, the AI-powered add-on for LiveNX, turns your network data into fast, guided answers, with value you can see in days.
LiveWire GEN3 device offerings
BlueCat LiveWire is a packet capture and network forensics platform that provides deep packet-level visibility across hybrid enterprise environments to help…
Get total control of your DDI infrastructure with Micetro’s unified API
Stop juggling between network tools and use Micetro’s RESTful API for complete control over your DDI infrastructure and cloud environment.
BlueCat MCP servers bring network intelligence to your AI assistant
Our MCP servers provide a standard integration layer that makes it easy to connect the AI tools you already use to BlueCat products.