The Power of a Client-Facing DNS Firewall
Learn why Adaptive DNS is the foundation for scalable, secure networks and critical to all of your digital transformation strategies.
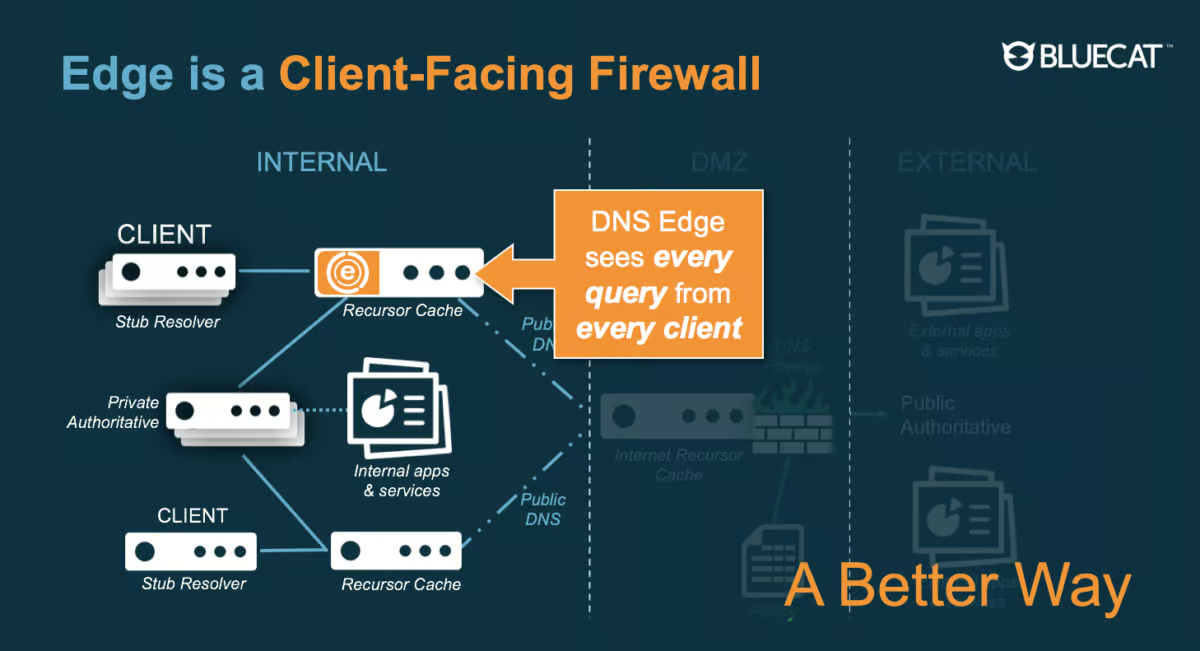
Read moreDNS filtering is a security control that allows, blocks, or redirects domain name queries at the resolver based on administrator policy and threat intelligence, stopping prohibited connections before they occur. Nearly every network connection begins with a DNS lookup, making the resolver an ideal enforcement point to centrally apply policy across all devices—including unmanaged, guest, and IoT equipment—without requiring security agents on individual endpoints. While DNS filtering effectively blocks phishing sites, malware hosts, and command-and-control domains early in an attack chain and provides query logs to identify suspicious activity, its effectiveness depends on proper management: stale block lists, overly broad categories, unmonitored bypass paths like encrypted DNS, and direct IP connections can create false positives, visibility gaps, and enforcement inconsistencies that undermine protection.
DNS filtering places a policy decision at the point where a client asks a resolver to translate a domain name into an IP address. The resolver checks the name against its rules before it answers.
Filtering only covers traffic that uses the filtering resolver. Clients that connect directly to an IP address, or that send queries to an outside resolver, including through encrypted DNS, can bypass it unless the network restricts those paths. Filtering also judges only the name, not page content.
Devices configured with a hardcoded public resolver, or browsers using DNS over HTTPS, skip the filtering resolver entirely. Blocked sites then load normally for those clients, and the query logs show nothing for them.
Broad category rules or stale block lists can block legitimate sites, content delivery domains or software update hosts. Users report that applications fail or pages load partly, and the cause is found only by searching query logs for the blocked name.
When queries pass through an intermediate forwarder or NAT device, the filtering resolver sees only that device's address. Policy by user or group cannot be applied, and logs cannot identify the originating host.
Clients and downstream resolvers keep answers until the record's time to live expires. A newly added block can take effect late for names already cached, which looks like inconsistent enforcement during testing.
Malware that connects to a hardcoded IP address never issues a lookup, so DNS filtering never sees it. Teams relying only on the resolver miss this traffic unless firewalls or other controls also cover it.