What is DNS poisoning (DNS spoofing) and how to prevent it
DNS poisoning (aka DNS cache poisoning or DNS spoofing) uses security gaps in the DNS protocol to redirect internet traffic to malicious websites.
Read moreDNS spoofing is a security attack that supplies falsified DNS answers to redirect domain names to attacker-controlled IP addresses, either by forging responses or altering cached DNS data. This threat is particularly dangerous for enterprises because a single forged record in a recursive resolver's cache can affect every client using that resolver until the entry expires, enabling credential theft, malware delivery, and traffic interception without requiring changes on client systems. Prevention requires deploying DNSSEC validation, using randomized source ports and query IDs, restricting recursion to trusted clients, and maintaining patched resolver software alongside encrypted transport mechanisms like DNS over TLS.
DNS spoofing succeeds when a resolver or client accepts a forged answer as genuine. The most common form targets a recursive resolver and its cache, so one false answer can affect every client that uses that resolver.
Spoofing can also happen without racing responses, for example by compromising a DNS server, changing zone data, or intercepting traffic on the network path. Validating answers with DNSSEC, randomizing source ports and query IDs, and restricting who can change DNS data reduce the risk.
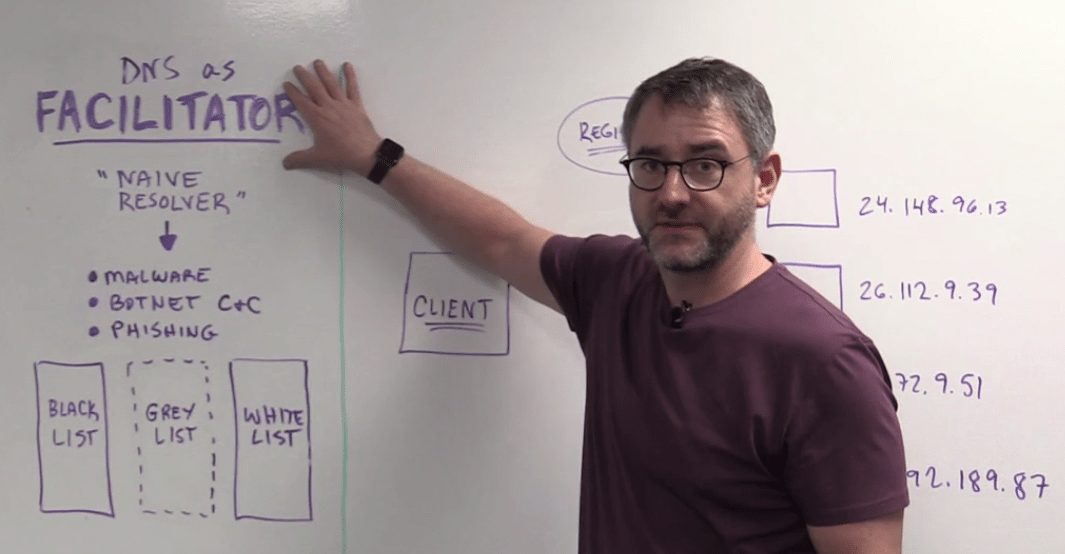
Spoofing can also target recursive resolvers, forwarders and internal caches. A corporate resolver that accepts bad data can affect every client behind it.
TLS with valid certificate checking limits the harm of a redirect, but it does not stop the false DNS answer. Users who click through certificate warnings, or applications that skip validation, remain exposed, and non-web traffic such as email may not be protected.
DNSSEC lets a validating resolver reject forged data for signed zones. It does nothing for unsigned zones, and it protects clients only if the resolver validates and the path between client and resolver is trusted.
Clearing a poisoned cache removes the bad entry but not the cause. If the resolver is still exposed, with predictable query attributes or open recursion, the attacker can poison it again.
The user usually sees the correct name in the address bar. Only the IP address behind it is false, so visual inspection of the domain rarely reveals the attack.