
Blog
DNS glossary

 Key takeawaysKey takeaways are generated with AI assistance. Because automated summaries can occasionally contain errors or miss important context, always refer to the full blog post for complete information.
A non-recursive query, also called an iterative query, is a DNS request that asks a name server to provide only the information it already holds or to refer the client to another server, without performing additional lookups on the client's behalf. Non-recursive queries form the backbone of DNS traffic between servers, with recursive resolvers using them to walk the DNS hierarchy by querying root servers, top-level domain servers, and authoritative servers in sequence. Understanding the distinction between recursive and non-recursive queries is operationally critical for server design, troubleshooting, security configuration, and preventing misconfigurations such as stub clients pointed at authoritative-only servers that refuse recursion.
In a non-recursive query, the client sends a question and the server replies with the best information it has, without doing further lookups on the client's behalf. Recursive resolvers use this approach to walk the DNS hierarchy.
The server never queries other servers for the client, so the work of following referrals stays with the asker. A resolver typically starts at a root server, then queries a top-level domain server, then the authoritative server for the domain, using non-recursive queries at each step.
Iterative queries are not inherently slower. Each step is a simple lookup, and a resolver that caches referrals and answers often skips most of the steps.
Stub resolvers normally send recursive queries to a resolver. The non-recursive exchange happens between the resolver and authoritative servers, so it is mostly invisible to end clients.
A referral is a normal response, not a failure. It points the resolver to name servers closer to the answer, and a missing referral is a delegation problem rather than a query-type problem.
An authoritative-only server does not resolve names outside its zones, even when the recursion desired flag is set. It typically returns a referral or a refusal, which is often mistaken for an outage.
A caching server can answer a non-recursive query from its cache if the data is there. If it is not cached, the server does not go and fetch it for that query.

 Article
A recursive query is a DNS query in which the DNS server retrieves the answer by querying other DNS servers on behalf of the requester and returns the result.
Article A recursive DNS server is the first server contacted by a requesting host; it retrieves the proper IP address of the intended domain name and returns it to the requester.
Article An authoritative DNS server provides original and definitive answers to DNS queries.
Article A DNS query is a request for information sent from a device to a DNS server asking it to resolve a domain name.
Article A DNS namespace is the hierarchical structure of domains that form a complete domain name in the DNS system.
Article DNS delegation is the process of assigning responsibility for managing a domain or subdomain to separate authoritative DNS servers.
Article The Domain Name System (DNS) is a hierarchical naming system that resolves domain names to IP addresses, enabling communication across network devices.
Every DNS query gets a response. Stay on top of your network activity with BlueCat by understanding the four most common DNS response codes.
Read more
At a basic level, an NXDOMAIN response means “that site does not exist.” But it can also provide critical clues about your network’s security.
Read more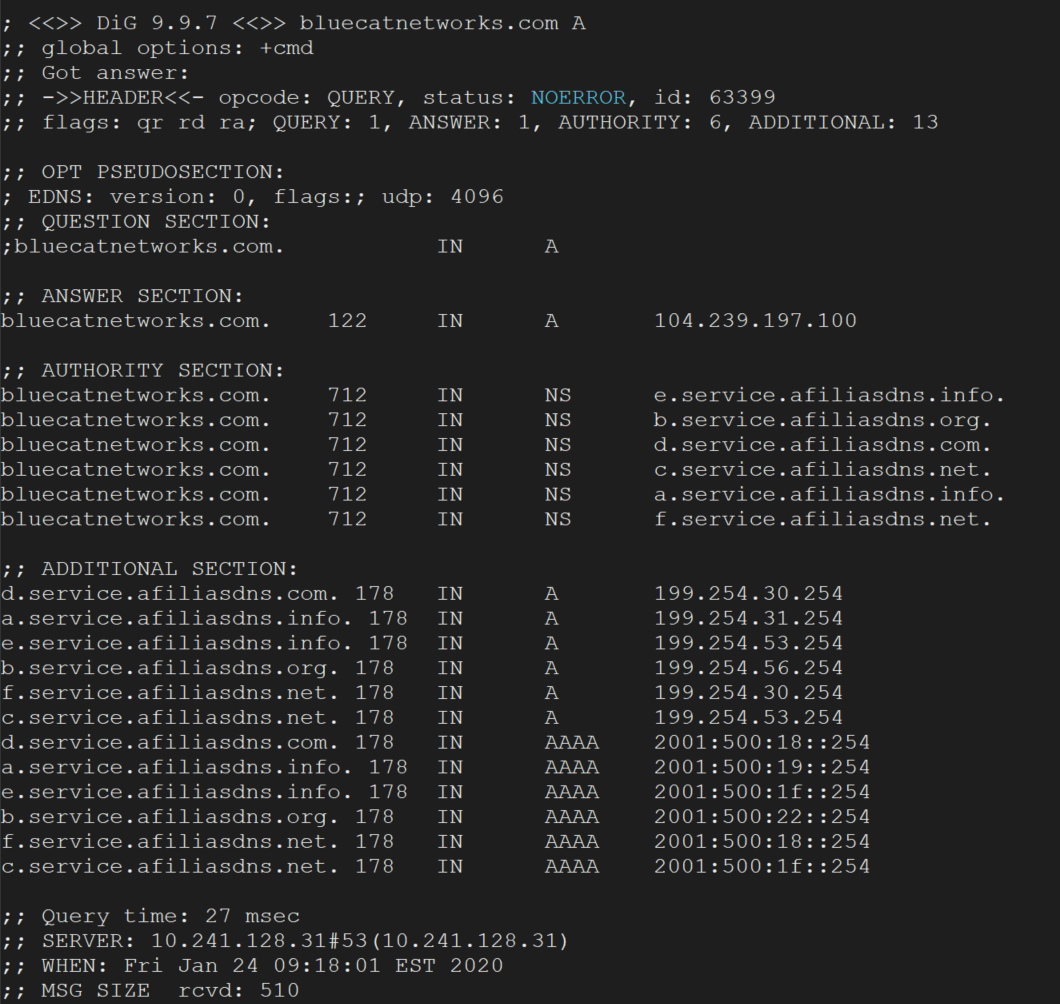
There are dozens of DNS record types. Understanding the most common ones can help you detect threats and keep on top of what's happening…
Read more
Many factors affect how you decide to set time to live (TTL) for DNS servers. Learn more, plus how BlueCat Edge's TTL features can…
Read more
DNSSEC authenticates DNS queries and responses by using cryptographic digital signatures. Learn more and how BlueCat can help to make implementation easier.
Read more